


Introduction
The telecom networks are evolving from 5G to 6G and adding new capabilities such as AI-native operations, autonomous UE AI agents, integrated sensing, NTN and distributed data frameworks. These new capabilites will introduce new security challenges. Unlike 5G, 6G will require a broader security architecture to protect emerging network entities, interactions and trust relationships beyond conventional authentication, encryption and integrity protection.
The 3GPP SA3 working group is investigating these challenges unsder technical study 3GPP TR 33.801-01, Study on Security for the 6G System, Release 20. Version 0.7.0 (October 2026) explores security aspects covering RAN, UE-to-Core communication, SBA, authentication and authorization, AI agents, data frameworks, sensing, NTN, and security monitoring.
This blog examines these areas, focusing on potential security mechanisms, technical challenges and implications for 6G system design and protocol development.
Overview of 6G Security Areas
The study has identifies following eleven major security areas. These areas demonstrate that 6G security is not limited to protecting radio and core-network interfaces. It also needs to address the trustworthiness of AI-driven entities, distributed data services, sensing operations and communication across different network domains.
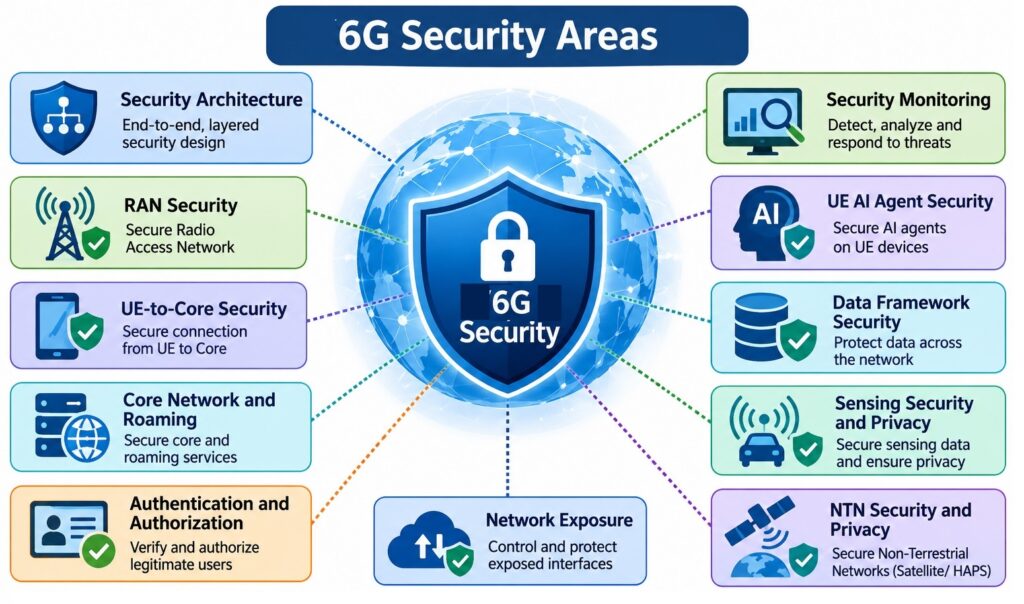

- Security Architecture: Security domains, trust anchors and key hierarchy
- RAN Security: MAC control element protection, mobility and initial RRC security
- UE-to-Core security: NAS protection and generic UE-to-CN communication
- Core Network and Roaming: SBA authorization, interconnect and trust management
- Authentication and Authorization: Subscriber authentication, identity privacy and access authorization
- Network Exposure: Secure exposure of network capabilities and APIs
- Security Monitoring: Security-event collection, attack detection and response
- UE AI Agent Security: Authentication, authorization and secure AI-agent communication
- Data Framework Security: Authentication and authorization of data producers and consumers
- Sensing Security and Privacy: Protection of sensing services and sensing-related information
- NTN Security and Privacy: Security across terrestrial and non-terrestrial network environments
6G Security Architecture
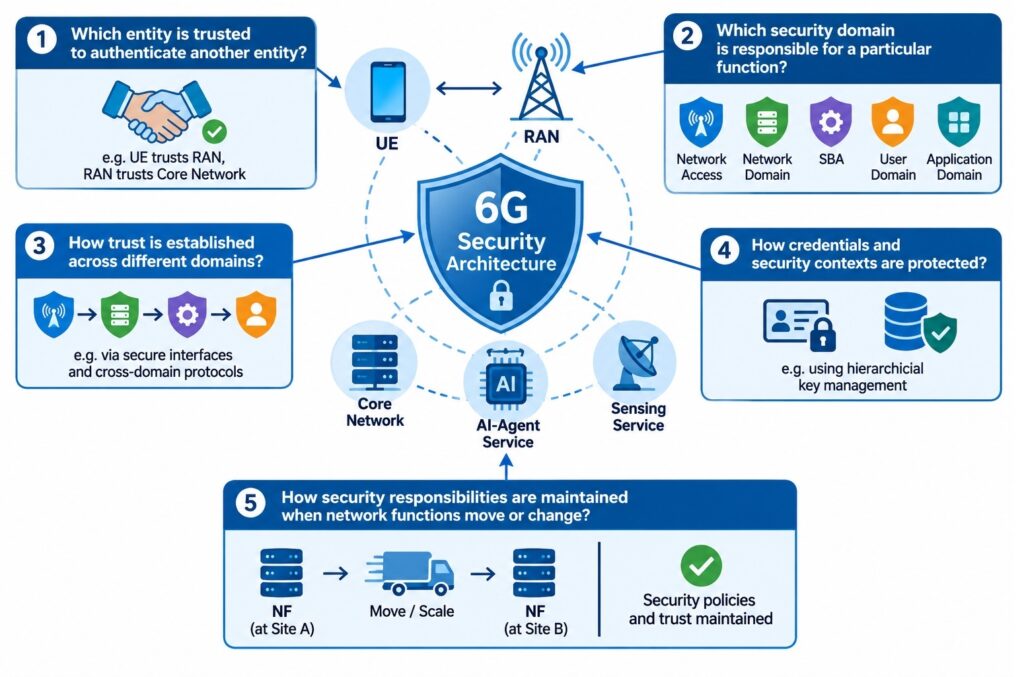
The security architecture creates trust between network entities and protects communication across network domains. In 5G, security domains isolate administrative, functional and deployment boundaries, including network access, network domain, SBA, user and application security.
The 6G study explores how these domains and their trust anchors should evolve to support the new architecture. These anchors are trusted entities or mechanisms used to validate identities, credentials and security contexts across different network entities, including UEs, RAN nodes, core networks, AI-agent services and sensing services.
The security architecture must establish trust anchors as shown in following figure. This becomes very important particularly in a distributed architecture where network functions may be deployed across multiple locations and administrative domains.

6G Security Key Hierarchy
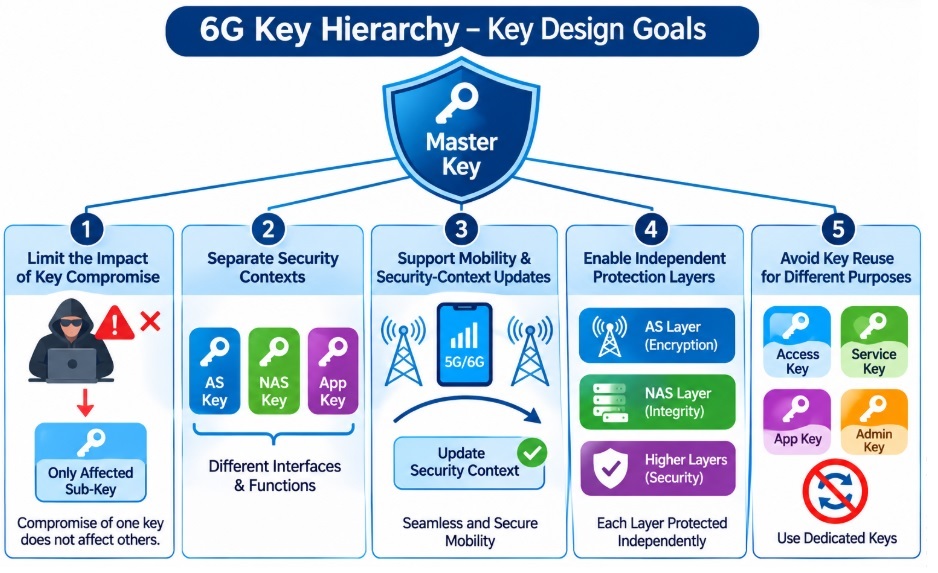
For any secure network, a well defined key hierarchy mechinism is required to protects the communication at different protocol layers. The 6G study investigates the key hierarchy and the security mechanisms needed for access-stratum (AS) and non-access-stratum (NAS) protection. The main key design goal is to establish appropriate cryptographic keys for different security purposes while maintaining separation between security contexts.
A hierarchical key management approach helps to acheive following goals. For 6G security architecture Key derivation, key activation, algorithm selection and security context lifecycle management etc. remains important parts.

Security algorithms and authenticated encryption
The study considers security algorithms for AS and NAS protection, including Authenticated Encryption with Associated Data (AEAD), which provides confidentiality and integrity while authenticating unencrypted associated data.
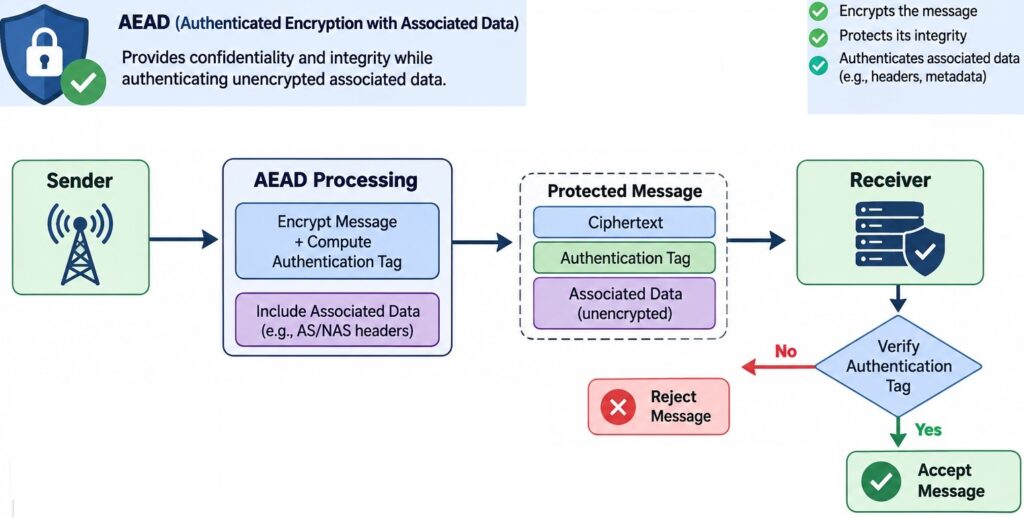

The receiver verifies the authentication tag before accepting a protected message. AEAD simplifies encryption and integrity protection but requires careful management of keys, nonces, counters and algorithm activation. The report also covers interim algorithm agreements, with detailed implementation aspects remaining subject to further study and standardization.
6G RAN Security
6G RAN security is a critical security component which is responsible for radio communication, mobility, scheduling and UE access. The 6G study focuses on the following key security aspects:
- MAC CE Security: Protecting MAC Control Elements.
- RAN Mobility Security: Securing communication during mobility procedures.
- Initial RRC Security: Protecting and validating initial RRC messages.
- Unicast RRC Security: Ensuring secure RRC signalling.
- UE State Transition Security: Maintaining security during UE state transitions.
UE-to-Core Network Security
UE-to-core network security focuses on protecting control signalling and operator-service interactions in the 6G architecture. The study examines NAS security, including single and multiple NAS security termination points, to avoid unauthorized reading, modification, message injection and replay attacks. Key requirements include confidentiality, integrity, replay protection, secure algorithm selection and key activation.
The study also investigates how NAS functionality should be terminated within the 6G core network. When multiple network functions process NAS signalling, security mechanisms must ensure consistent protection and avoid security gaps across different entities.
For generic UE-to-core interactions, 6G explores different signalling options, including control-plane, user-plane or new-plane transport mechanisms for control and operator-service signalling. Regardless of the selected architecture, confidentiality, integrity and replay protection must be maintained, with coordinated security mechanisms for NAS and non-NAS signalling.
Core Network and SBA Security
The 6G core network continues to use service-based interactions between network functions (NFs). The study focuses on strengthening trust and authorization in SBA, ensuring that authentication verifies an NF’s identity while authorization controls its access to specific services considering following.
- Linking Network-Function Authentication to Authorization: The 6G study focuses on securely linking network-function (NF) authentication with access-token authorization. It explores OAuth-based mechanisms and DPoP to ensure that authenticated NF identities match the identities associated with authorization tokens, preventing token misuse.
- DPoP-Based Access-Token Protection: The study explores DPoP to strengthen access-token security and prevent replay attacks. The consuming NF (NFc) requests an access token from the NRF with a DPoP proof. After verification, the NRF issues the token. The NFc then sends the token and a fresh DPoP proof to the producer NF (NFp), which verifies both before processing the service request.
- Access-Token Revocation: The study considers efficient access-token revocation when an NF loses authorization or a security incident occurs. The objective is to invalidate compromised or unauthorized tokens before expiry while minimizing signalling and processing overhead in distributed core networks.
- Additional SBA Security Topics: Other SBA security areas include access-token sender verification, audience restriction, NF-set-level tokens, credential confidentiality, distributed authorization, separation of authentication and authorization endpoints, and trust-anchor/root-CA certificate exchange across security domains.
Subscription Authentication and Identity Privacy
Subscriber authentication remains a key security requirement in 6G. The study builds on 5G primary authentication and key agreement while investigating new threats to subscriber identity privacy and authentication.
- Identity-Probing and Linkability Attacks: The study examines identity-probing attacks using replayed RAND/AUTN authentication challenges and SUCI manipulation. Attackers may exploit differences in UE authentication responses to identify or track subscribers and infer their presence in a particular location.
- Potential Security Requirements: The study identifies the need for secure primary authentication and key agreement across 3GPP and non-3GPP access, along with mechanisms to prevent identity-probing, SUCI replay and substitution attacks while protecting subscriber privacy.
- Non-3GPP Access Authentication: 6G will support different access technologies, including non-3GPP access. The study explores new security requirements beyond existing 5G assumptions, with particular focus on mutual authentication between the UE and network.
- Non-Seamless WLAN Offload: Non-Seamless WLAN Offload (NSWO) enables UEs to access WLAN using 3GPP subscription credentials. The study considers EAP-based authentication, building on the 4G/5G EAP-AKA‘ approach, while maintaining subscriber identity privacy and minimizing repeated full authentications with the 6G core.
Security Monitoring and Incident Response
In 6G, Security monitoring aims to detect abnormal behaviour and attacks, which include involvement of valid but stolen credentials that may not trigger authentication failures. The study highlights the need to collect and correlate security events across network functions to identify suspicious API calls and anomalous activities, using security related events defined in 3GPP TS 33.502 as a baseline.
Under this, Distributed Security Response Study examines a coordinated response framework to mitigate detected threats across affected network entities. Possible actions include threat remediation, malicious traffic redirection and handling suspicious API calls. Communication between security-monitoring functions and network entities must be protected through confidentiality and integrity mechanisms to prevent forged mitigation instructions and avoid impacts on network availability.
UE AI Agent Security and Privacy
6G introduces UE AI agents that can autonomously discover services, communicate with other agents and access network capabilities. The study highlights the need to establish trust in these agents and ensure they perform only authorized operations.
- Secure Communication Between AI Agents and the Network: The study focuses on securing communication between UE AI agents and the 6G core during registration, discovery, agent communication and network-service interactions. Confidentiality, integrity and replay protection are essential to prevent unauthorized access, message modification and replay attacks.
- AI-Agent Authorization: The study emphasizes separating authentication from authorization. While authentication verifies the AI-agent identity, authorization determines its permitted services and capabilities. Authorization information must be securely bound to the requesting agent to prevent one agent from misusing another agent’s permissions.
- Authorization of AI-Agent Intents: 6G must ensure that AI-agent intent-based requests are authorized before being translated into network actions. The study considers authorization of service access, lifecycle-based updates and revocation of permissions, and binding authorization information to the correct agent identity. This prevents AI agents from gaining unauthorized privileges through intent-based requests
Data Framework Security
The 6G data framework enables interactions between data producers, consumers and framework services. The study highlights the need for authentication to ensure trusted data exchange and prevent unauthorized access or data publication.
In this framework, Authentication of Data Producers and Consumers study identifies mutual authentication between the data framework and data producers, as well as between the framework and consumers, as a potential security requirement. Direct producer-consumer authentication and the UE’s role as a data producer or consumer remain subject to architectural decisions.
Sensing Security and Privacy
Integrated sensing and communication introduces new security and privacy requirements in 6G. The study focuses on authorization and revocation for sensing-service consumers, along with protecting operations between sensing functions and entities.
- Sensing-Service Authorization: Sensing-service consumers must access only authorized services, with mechanisms to revoke permissions when required. This is important because sensing data may reveal information about the surrounding environment and activities.
- Protection of Sensing Operations: The study highlights the need to establish trust between sensing functions and entities and protect their service interactions. Sensing-signal security and privacy remain areas for further study, rather than finalized mechanisms.
NTN Security and Privacy in 6G
6G NTN introduces security challenges involving satellites, terrestrial networks and different connectivity scenarios. The study considers terrestrial–non-terrestrial service continuity, inter-PLMN continuity, multi-orbit access and mobility-related security.
- Security Across Terrestrial and Non-Terrestrial Networks: When a UE switches between terrestrial and non-terrestrial access, authentication, authorization and security contexts must be handled securely to maintain service continuity and trusted communication.
- Multi-Orbit and Mobility Scenarios: Changes in satellite access and orbit conditions introduce additional challenges for security-context management and service continuity. The study identifies these as areas for further work. Protocol testing should therefore consider the continuity and correctness of security procedures during NTN access changes.
Conclusion
The 3GPP TR 33.801-01 study highlights key security challenges being explored for 6G, extending beyond conventional UE authentication and network protection. Major areas include RAN and SBA security, subscriber privacy, AI-agent authorization, data-framework authentication, sensing protection, NTN security, and distributed monitoring and incident response.
The key takeaway for telecom engineers is that 6G security must cover the complete network lifecycle, from identity management and authentication to authorization, mobility, monitoring and incident response. As the study is still evolving, its proposed mechanisms and open issues require further investigation before becoming finalized implementation requirements.
References
- 3GPP TR 33.801-01 V0.7.0 (2026-10), Study on Security for the 6G System (Release 20).
- 3GPP TS 33.501, Security architecture and procedures for 5G System.
- 3GPP TS 29.500, 5G System – Technical Realization of Service Based Architecture.
- 3GPP TS 29.510, Network Function Repository Services.
- IETF RFC 9449, OAuth 2.0 Demonstrating Proof of Possession (DPoP).
- 3GPP TS 33.502, Security-related Events Handling.